Policy Based Routing (PBR) on HPE Aruba ArubaOS-Switch
How to configure Policy Based Routing on HPE Aruba ArubaOS-Switch (3800, 5400, 8200 series) to route traffic to different next-hops based on source and destination, with an important note on locally connected networks.
How to configure Policy Based Routing (PBR) on HPE Aruba ArubaOS-Switch. Applies to the 3800, 5400zl v2, and 8200 series. PBR can only be applied inbound.
Three components: a class to match traffic, a policy to define the action, and a VLAN/port to apply it.
Scenario #
Traffic from 192.168.10.0/24 to 10.0.0.0/24 uses gateway 2.2.2.1. All other traffic uses 1.1.1.1.
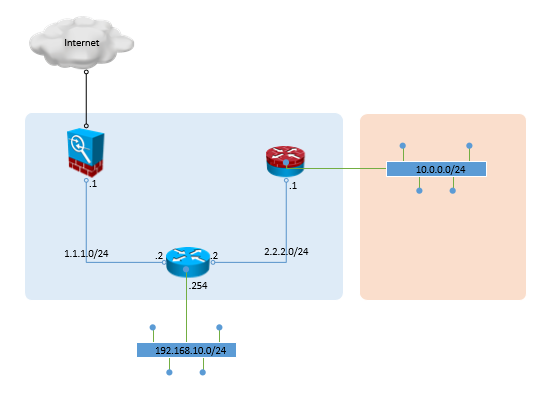
Class configuration #
class ipv4 "CLASS-192.168-LOCAL-BREAKOUT"
 5 match ip 192.168.10.0 0.0.0.255 10.0.0.0 0.0.0.255
 exit

class ipv4 "CLASS-192.168-INTERNET-BREAKOUT"
 5 match ip 192.168.10.0 0.0.0.255 0.0.0.0 255.255.255.255
 exit
Policy configuration #
policy pbr "POLICY-INTERNET-BREAKOUT"
 5 class ipv4 "CLASS-192.168-LOCAL-BREAKOUT"
  action ip next-hop 2.2.2.1
  exit
 6 class ipv4 "CLASS-192.168-INTERNET-BREAKOUT"
  action ip next-hop 1.1.1.1
  exit
 exit
Apply to VLAN interface #
vlan 10
 name "192.168.10.0-VLAN"
 ip address 192.168.10.254 255.255.255.0
 service-policy "POLICY-INTERNET-BREAKOUT" in
 exit
Important: locally connected networks #
If other VLANs are on the same switch, PBR will break inter-VLAN routing because it overrides the routing table for matched traffic. Fix this by pointing the local class next-hop at the switch’s own IP:
policy pbr "POLICY-INTERNET-BREAKOUT"
 5 class ipv4 "CLASS-192.168-LOCAL-BREAKOUT"
  action ip next-hop 192.168.10.254
  exit
 6 class ipv4 "CLASS-192.168-INTERNET-BREAKOUT"
  action ip next-hop 1.1.1.1
  exit
 exit
With default gateway ip route 0.0.0.0 0.0.0.0 2.2.2.1, this restores inter-VLAN routing while still sending internet traffic to 1.1.1.1.